Beyond Firewalls: Why K-12 Cybersecurity Education Must Target the Human Element
By EdTech Insights Desk
Published: October 2023
Main Facts: The Frontline of K-12 Cybersecurity
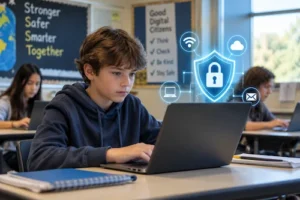
In an era defined by digital-first instruction, cloud-based classrooms, and ubiquitous connected devices, K-12 schools find themselves on the front lines of a constantly shifting cyberthreat landscape. While district leaders invest heavily in technological defenses—deploying sophisticated firewalls, identity protection software, endpoint security, and multifactor authentication—a critical vulnerability remains: the human sitting in front of the screen.
According to the U.S. State of EdTech 2026 report by the Consortium for School Networking (CoSN), which surveyed more than 600 education technology leaders across 44 states, cybersecurity remains the single highest technology priority for school districts. However, the report also highlighted a glaring systemic vulnerability: 65 percent of educational technology leaders identified insufficient cybersecurity staffing and a lack of dedicated budgets as their leading barriers to addressing these compounding challenges.
Technical controls are indispensable, but they cannot make every split-second decision for a student or staff member. Eventually, an individual receives an unexpected message, encounters a deceptive link, shares sensitive information, or is prompted to log into a familiar-looking portal. At that exact juncture, technology steps back, and human judgment takes center stage.
As cyberthreats continue to evolve—supercharged by generative artificial intelligence capable of producing hyper-realistic phishing emails, deepfake audio, and flawless corporate impersonations—educators and IT professionals argue that basic rule-memorization is no longer enough. Cybersecurity education must transition from a passive set of static warnings into an active, experiential component of modern digital literacy.
Chronology: The Evolution of School IT and the Rise of the Human Vulnerability
To understand how K-12 cyber defense reached its current inflection point, it is instructive to look at the historical trajectory of school network management over the past two decades.
- The Early 2000s (Perimeter Defense Era): School district networks were largely self-contained environments. Security focused on basic perimeter controls, content filtering, and physical server rooms. Threats were predominantly external viruses or basic malware spread via physical media like floppy disks and USB drives.
- The 2010s (Cloud Migration and One-to-One Devices): As districts embraced "one-to-one" device initiatives—providing every student with a laptop or tablet—networks expanded exponentially. Educational institutions moved administrative systems and learning management platforms to the cloud, dramatically increasing their digital attack surface.
- The 2020–2022 Pandemic Pivot (Hyper-Dependency): Emergency remote learning forced schools to rely entirely on digital infrastructure overnight. While educational continuity was preserved, cybercriminals recognized the vulnerabilities inherent in rushed, decentralized deployments. Ransomware attacks against K-12 school districts surged nationwide, disrupting operations, exposing student data, and costing millions in remediation.
- 2023–Present (The Generative AI and Sophisticated Phishing Era): Modern cyberattacks no longer rely on poorly worded emails with obvious spelling mistakes. The proliferation of generative AI tools allows bad actors to orchestrate highly targeted, contextually accurate phishing campaigns that routinely bypass traditional human suspicion. Concurrently, reports like CoSN’s U.S. State of EdTech 2026 have formalized what IT veterans have long observed: technology alone cannot bridge the gap between escalating threats and constrained human defenses.
Supporting Data: The Scale of the Challenge
Data from educational technology benchmarks and national cybersecurity agencies underscore the urgency of rethinking how schools approach digital safety.
- 65 Percent: The percentage of ed-tech leaders who cite insufficient cybersecurity staffing and a lack of dedicated funding as their primary barriers to securing school networks, according to the CoSN U.S. State of EdTech 2026 report.
- Number One Priority: Cybersecurity’s ranking among educational technology leadership, outstripping hardware upgrades, remote learning tools, and administrative software integration.
- 1,200 to 2,300 Students: The scale of typical secondary school environments—such as Ken Stimpson Community School and South Hunsley School in the United Kingdom, where IT management insights have underscored that technical infrastructure must be paired with human behavioral training to manage systemic risk at scale.
- Countless Daily Decisions: The sheer volume of digital choices made by students and staff every single day, ranging from password management and link verification to data sharing and multi-factor authentication prompts.
Official Responses and Expert Perspectives: Moving Beyond Compliance
Security frameworks from national bodies and field experts emphasize that technical controls must be supported by a culture of shared responsibility.
The Cybersecurity and Infrastructure Security Agency (CISA), in its comprehensive Protecting Our Future report on K-12 cybersecurity, outlines a clear mandate for school leaders. CISA stresses that establishing and reinforcing a cybersecure culture is a collective responsibility. Information technology and cybersecurity personnel cannot—and should not—carry the entire burden of defense alone. Students and staff must be active participants in that culture, rather than passive users merely sheltered by invisible administrative barriers.
Paul Cuffe, an IT and network professional with more than two decades of experience across educational, enterprise, and public-sector technology, argues that traditional educational methods fail because they treat cybersecurity as a compliance checklist rather than a cognitive skill.
"Students are already making cybersecurity decisions every day," notes Cuffe, creator of educational projects focused on interactive learning and technology careers. "Giving them a list of rules is not the same as teaching them how to recognize a threat. Most students have heard basic online safety advice—do not share your password, do not click suspicious links. The challenge begins when the threat does not look suspicious."
Cuffe points out that generative AI has democratized deception. Phishing messages now routinely mimic familiar institutional logos, exploit recognized services, and manufacture artificial urgency—such as warning that an account will be disabled immediately unless credentials are updated. In these scenarios, rote memorization collapses, and critical thinking must take over.
To combat this, experts advocate for safe, simulation-based learning environments where students can experience realistic threat scenarios, make choices, analyze their mistakes, and learn from them without real-world consequences.
"If a student makes the wrong choice during a simulated exercise, no account has been compromised and no data has been lost," Cuffe explains. "Instead, the mistake becomes the lesson. The individual threat will change, but the habit of stopping and asking, ‘Why should I trust this?’ has much more staying power."
Implications: Integrating Cybersecurity into Digital Literacy
As school districts grapple with severe staffing and budget constraints, the integration of cybersecurity education into existing frameworks is not merely an option—it is a strategic necessity.
1. Re-framing Cybersecurity as a Core Literacy
Practical cybersecurity education cannot remain sequestered within advanced computer science classes or specialized technology electives. Just as digital literacy encompasses media evaluation, information sourcing, and responsible online communication, foundational cyber judgment must be woven into the broader academic experience. Virtually every student will rely on online accounts, cloud-based educational platforms, financial portals, and connected devices throughout their personal and professional lives.
2. Low-Barrier Implementation for Crowded Curricula
A common hesitation among educators is the lack of room in an already packed academic calendar for a dedicated cybersecurity curriculum. However, subject matter experts emphasize that effective training does not require an entire semester-long course or specialized hardware laboratories.
- Ten-Minute Case Studies: Teachers can spend a brief window of class time comparing two emails, asking students to evaluate which one they trust and articulate their reasoning.
- Scenario-Based Problem Solving: Classrooms can walk through hypothetical situations where a user has inadvertently clicked a compromised link, discussing the immediate steps required for remediation.
- Information Verification: Students can examine online claims, manipulated images, or unexpected digital requests, identifying verification checkpoints before accepting or sharing the data.
3. Cultivating Long-Term Cognitive Habits
Technology will continue to evolve at a relentless pace. Artificial intelligence, decentralized networks, and novel communication platforms will spawn threat vectors that security professionals cannot yet anticipate. Consequently, K-12 institutions cannot realistically prepare students for every single phishing email, impersonation scam, or deepfake they will encounter in their lifetimes.
Instead, the ultimate objective of K-12 cybersecurity education is behavioral and cognitive resilience:
- Pause before taking immediate action.
- Question unexpected requests for information, access, or credentials.
- Verify information through independent, trusted channels.
- Recognize when digital anomalies do not make logical sense.
- Know when to ask for help from IT professionals or trusted adults.
By shifting the paradigm from passive protection to active, experiential learning, schools can transform students from potential targets into vigilant digital citizens—ensuring that a momentary lapse in judgment serves as an invaluable classroom lesson rather than a catastrophic institutional breach.